
Yes - data protection is a matter for the boss!


In dealing with data protection - both due to the new EU General Data Protection Regulation (GDPR) and the total revision of the national data protection law, there are many ambiguities. Although the topic of data protection is no longer present in the media on a daily basis, it remains in focus. In this workshop, the SDV wanted to demonstrate a pragmatic approach to the new data protection law with experts who have proven themselves in practice. Many executives are too little aware of what this new regime means for them and their company. To set the mood, we heard two keynote speeches and then the participants went through three different workshops on specific practical topics.
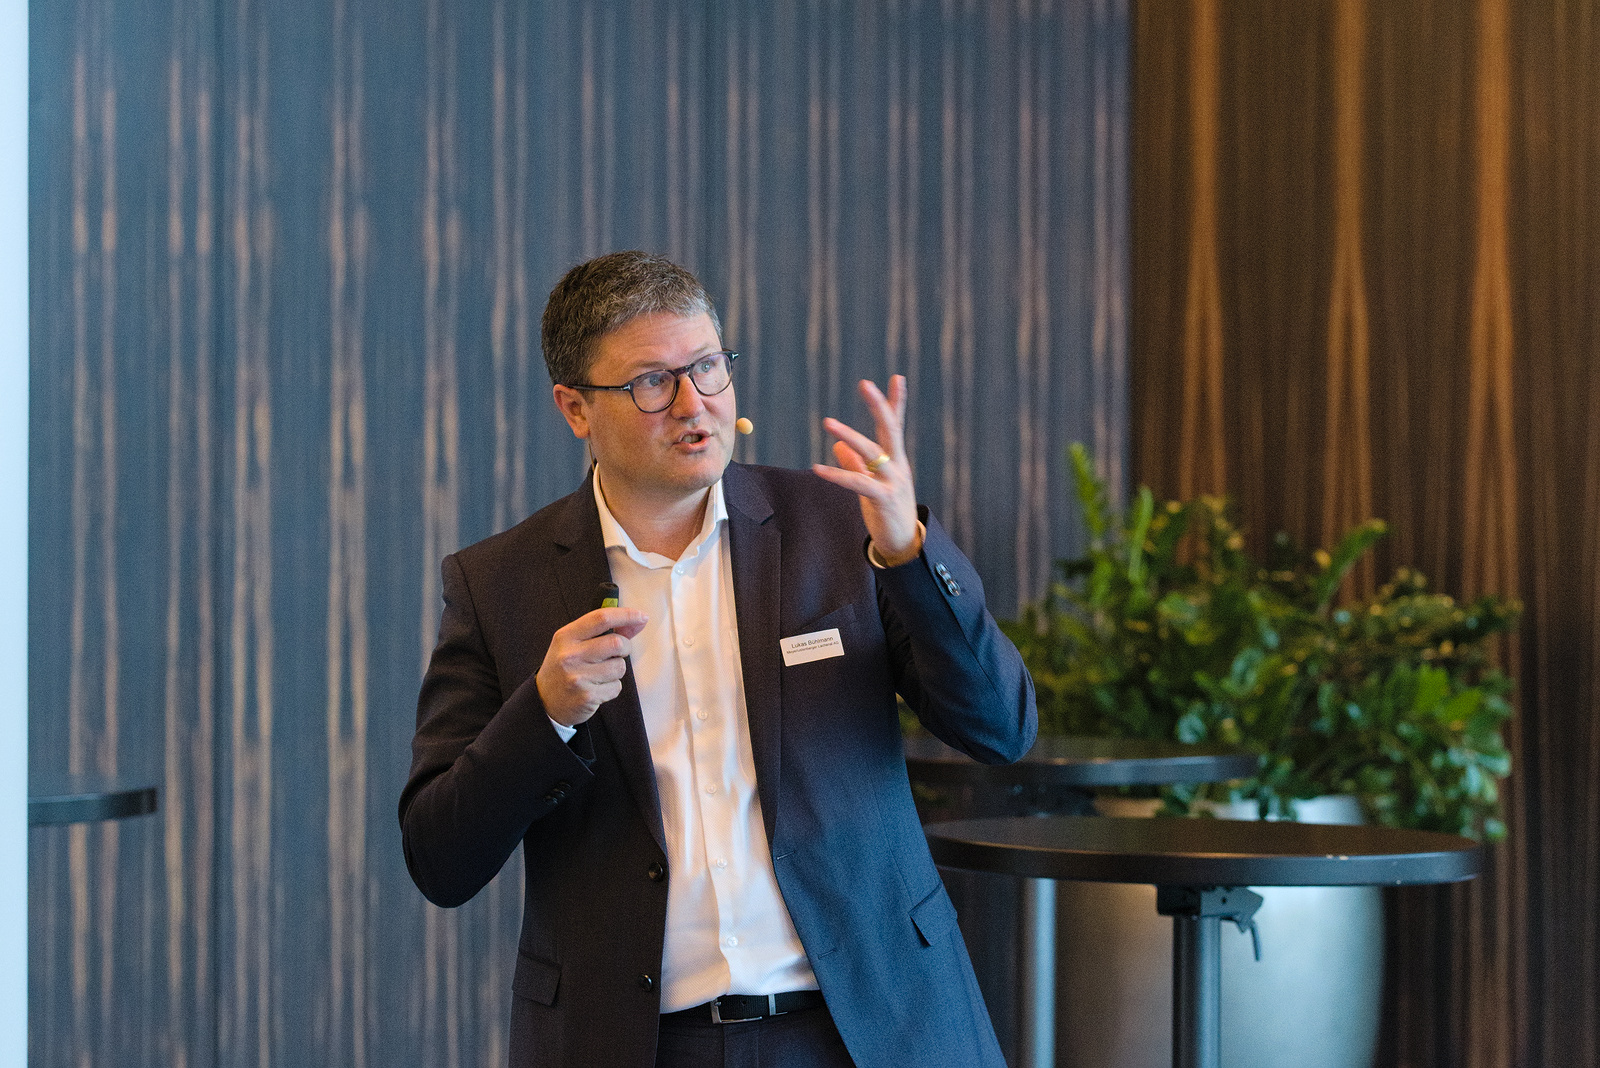
In the keynote speech by Lukas Bühlmann, partner at Meyerlustenberger Lachenal, entitled "Data Protection Law 2.0 The Opportunities of Data-Driven Marketing", the key messages were that modern marketing must be based on lawful and valuable data processing. The fact that not only the data protection law in the EU (DSGVO) but also the data processing principles of the expected Swiss data protection law must be complied with was explained using practical examples. With the influence of the data protection principles on direct marketing, cookies, the use of tracking and web analytics tools, social media , newsletter marketing and customer relationship management (CRM), a look into the near future was given.
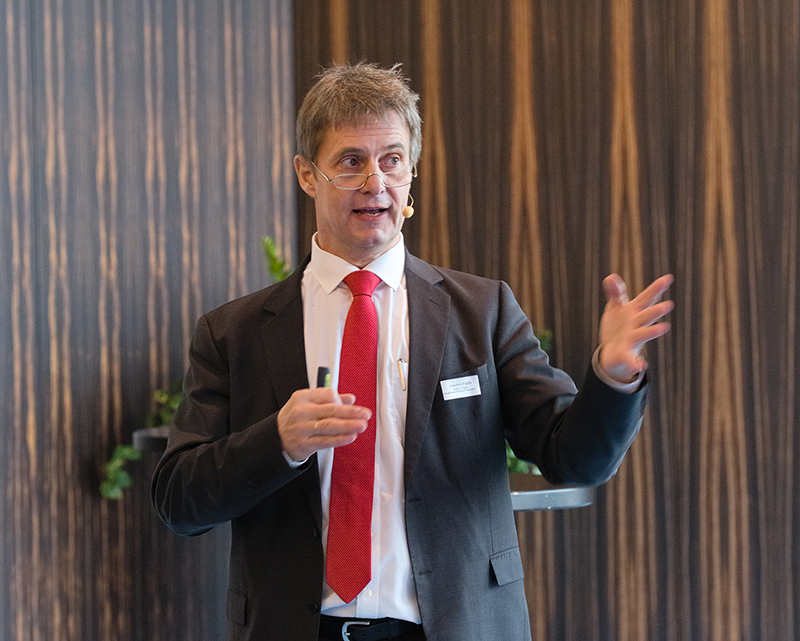
The keynote speech by Joachim Fauth, Head of Legal, Reader's Digest Germany/Switzerland/Austria "Experiences after 6 months of the GDPR data protection in digital dialog" showed us the problems regarding unclear definitions of information obligations and the high documentation effort based on first experiences in the practical handling of the GDPR. He also showed possibilities how dialog marketing is possible despite restrictions. As a board member of FEDMA, he spoke about the developments regarding the draft of the new ePrivacy Regulation of the EU, which primarily wants to restrict digital dialog marketing.
The form of the workshop should make it possible to determine the current situation, identify opportunities and risks, and give the participants concrete recommendations for action to take home.
Workshop topic 1
From the Excel list to the data protection management system (led by Roger Muffler). With the GDPR, the requirements for operational data protection have increased. An affected company must define, implement, document and control numerous measures. However, this task does not end with the implementation. The required documentation and processes and must be continuously updated and reassessed. The best way to do this is with a data protection management system (DSMS). In this workshop, Roger vividly described how to set up and operate a DSMS. From his own experience, he recommended sensitizing employees and accompanying them along the path from documentation to audit.
Workshop topic 2
The data protection statement as the linchpin of data protection compliance (led by Lukas Bühlmann). Transparent and comprehensible information about data processing has always been an important prerequisite for the lawful handling of customer or personal data. The ongoing reforms of data protection law in Europe and in other parts of the world clearly reinforce the central function of this information. In this workshop, it was specifically presented which information obligations exist and how these are to be included and depicted in particular within the framework of a data protection declaration. The central role of the data protection declaration and what is important from a practical point of view in the design, presentation and integration of this information tool was clearly explained by Lukas Bühlmann and discussed with the participants.
Workshop topic 3
Management is responsible for data protection (headed by Joachim Fauth)
In the GDPR and also in the new DSG, the controller must be able to demonstrate compliance with data protection regulations. In addition, the compliance measures must be documented including privacy policy, data protection concept, privacy policy, website, order processing contracts with providers, TOMs and possibly also a data processing directory. Joachim explained in detail that a company's management sets the data protection level and that management must perform a risk analysis and take appropriate measures.
Conclusion
What is the remaining impression of the event and its participants? The workshops were evaluated as a valuable, practical supplement to the keynote speeches. Small and medium-sized companies know very well that the topic of data protection is important. But according to a recent study by the ZHAW, Swiss companies have a lot of catching up to do. (Study: Data protection in Swiss companies 2018 - ZHAW). According to this survey, SMEs hardly provide corresponding resources. Data protection officers are lacking in 70 percent of the companies surveyed. This impression was confirmed in the personal conversation after the workshop.
Data protection event was part of the Swiss Leadership Forum
With more than 500 registered guests, the organizer of the Swiss Leadership Forum draws a positive balance. With "It's About Time ...", different aspects of time were highlighted, which was extremely exciting and impulse-rich for the attending leaders from business, politics and administration. "We are very pleased with the way the event went and the feedback from the participants was very positive throughout," said Stephan Isenschmid, Managing Director of the Swiss Leadership Forum. Since 2004, the Swiss Leadership Forum has focused on knowledge transfer and inspiration, the exchange of experience and the cultivation of personal relationships. The premium event traditionally takes place in the Swiss business capital of Zurich. The next edition will take place on November 21, 2019, again at "The Dolder Grand" in Zurich.


